Effective Date: September 10, 2026 | Last Updated: September 10, 2026
COMEXCEL Data Retention and Account Deletion Policy establishes binding data lifecycles, archival schedules, and permanent cryptographic purging protocols across all enterprise communications services. This policy describes how subscriber accounts, call detail records (CDRs), voice media, business messaging, and user credentials are systematically retained or expunged across our Business VoIP & Cloud PBX Solutions, mobile applications (iOS and Android), and downstream cloud services.
This policy satisfies mandatory requirements under Apple App Store Review Guideline 5.1.1(v), Google Play User Data & Account Deletion Requirements, GDPR Article 17 (Right to Erasure), the California Consumer Privacy Act (CCPA/CPRA), FCC Section 222 (CPNI) regulations, and HIPAA Security Rule data disposal standards (45 CFR § 164.310(d)(2)(i)).
Mobile App Store Account Deletion Compliance
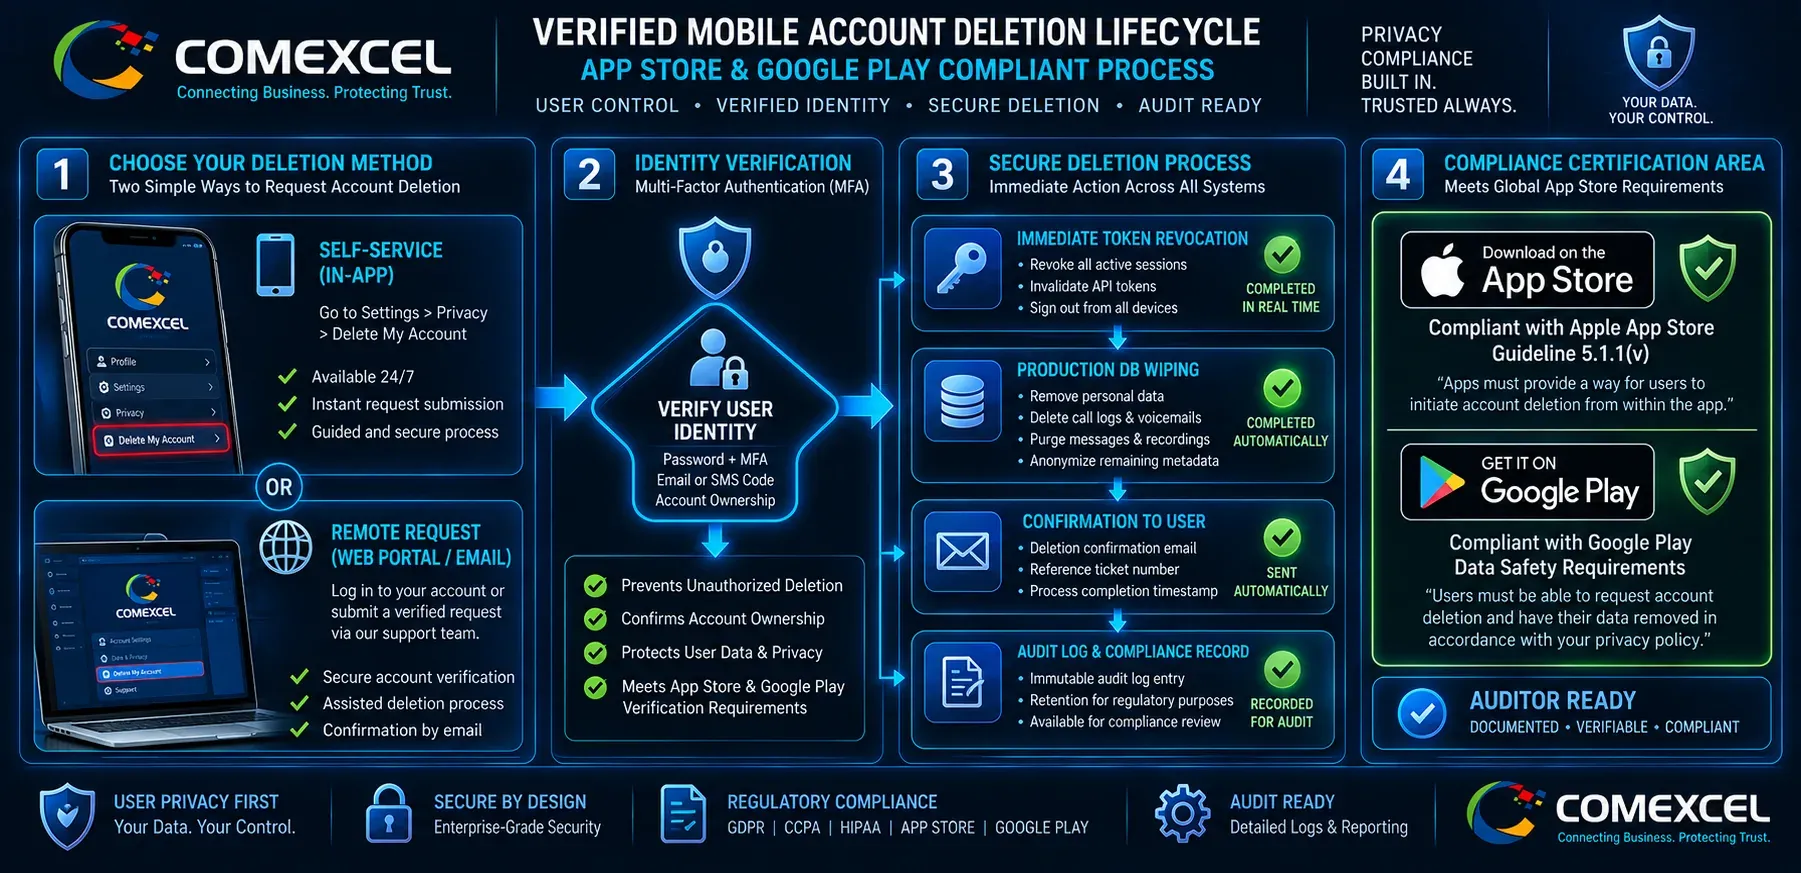
In accordance with Apple and Google Play store developer requirements, all users who create or access an account through the COMEXCEL Mobile Application (iOS/Android) have the absolute right to delete their account and associated personal data without being required to maintain an active subscription or keep the app installed. This policy operates directly alongside our master COMEXCEL Legal & Compliance Hub to enforce transparent data governance across all endpoints.
How to Delete Your Account
- Method A: In-App Self-Service Deletion (Instant)
- Open the COMEXCEL Mobile App on your iOS or Android device.
- Navigate to Settings → Account Profile → Security & Privacy.
- Tap “Delete Account & Associated Data”.
- Confirm your identity via multi-factor authentication (SMS/Email OTP code).
- Review the deletion summary and confirm the permanent purge request.
- Method B: Web-Based Deletion Request (Without Reinstalling the App)
- If you have uninstalled the app or cannot access your mobile device, submit a verified deletion ticket via the COMEXCEL Web Portal or email [email protected] with the subject line: “Data & Account Deletion Request”.
- State your verified Account Email, Business Account Number, and associated Phone Number.
- Requests submitted via web or email are acknowledged within 48 business hours and fully executed within 30 calendar days.
Standard Service Data Retention Schedule
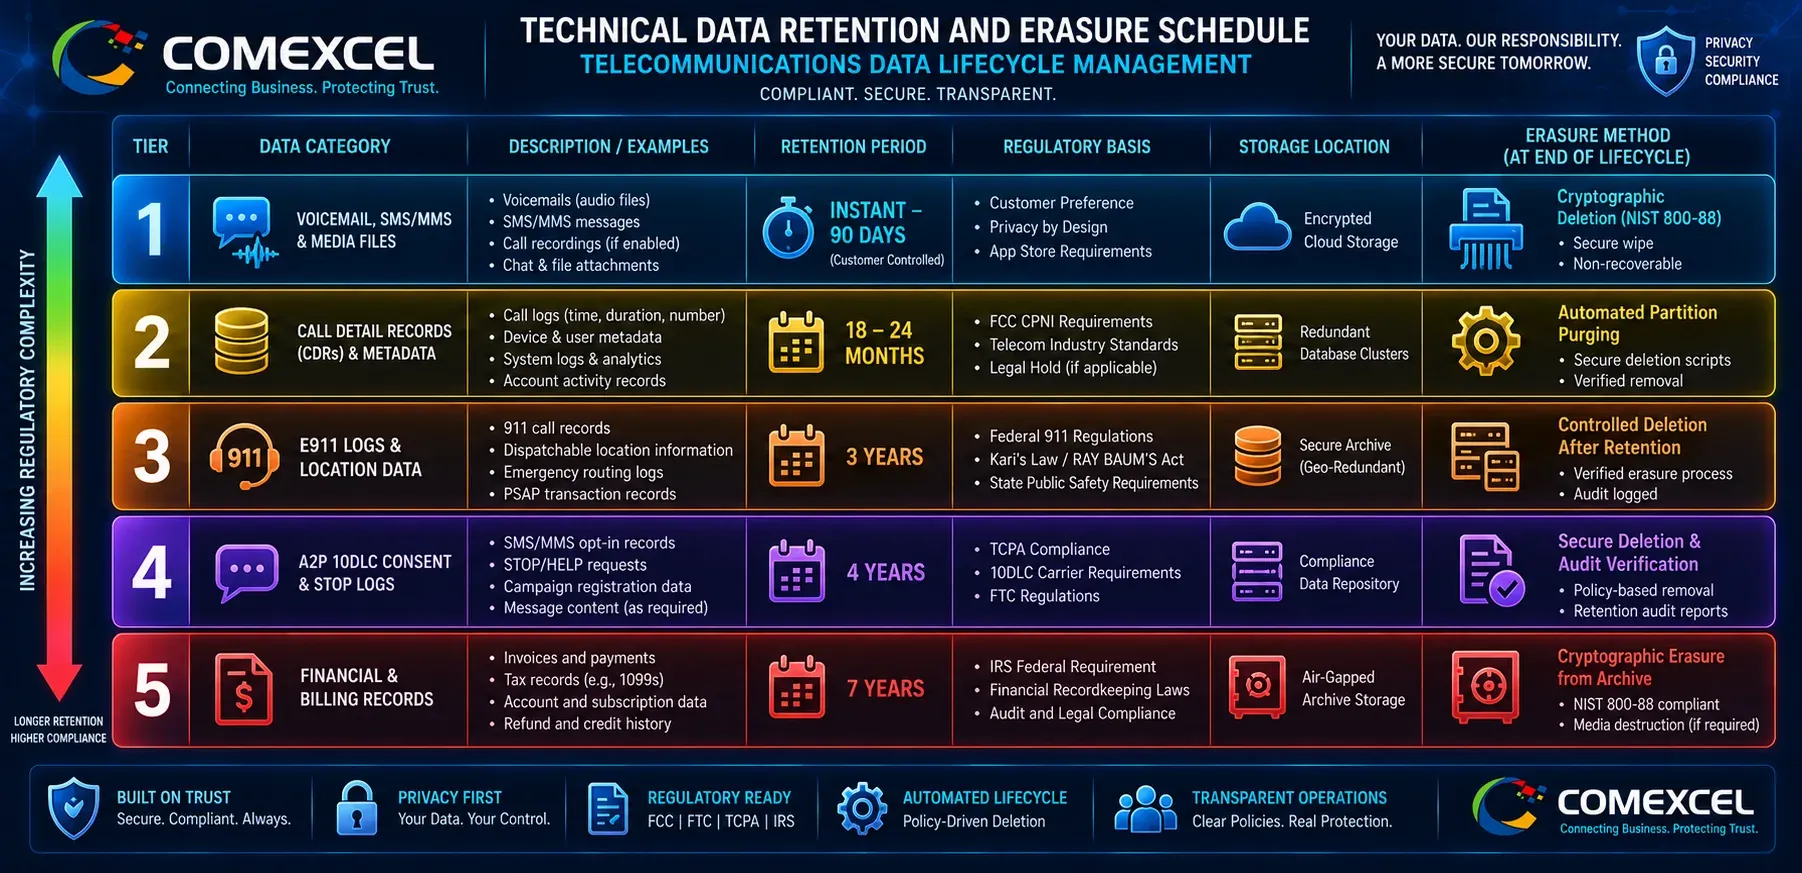
COMEXCEL retains data only for as long as necessary to provide services, fulfill contractual obligations, prevent fraudulent network abuse, and satisfy statutory record-keeping mandates:
| Data Category | Specific Data Elements | Standard Retention Window | Deletion & Purge Method |
|---|---|---|---|
| Account Credentials & Profile | Name, corporate email, login hash, authorized user list, and billing address. | Duration of active subscription + 30-day grace period post-cancellation. | Cryptographic purge from production DB; overwritten in backups within 30 days. |
| Call Detail Records (CDRs) | Originating/terminating phone numbers, time, duration, call routing, and SIP status codes. | 18 to 24 Months (FCC billing dispute and CPNI regulatory requirement). | Automated cron purge; partitioned tables sanitized according to NIST SP 800-88 R1. |
| Voice Media & Recordings | Call recordings, voicemail audio files, and Interactive Voice Response (IVR) audio assets. | Customer Defined (Default: 30 to 90 days, or instant deletion via admin portal). | Immediate file unlinking; AES-256 storage blocks zeroed and cryptographically shredded. |
| SMS / MMS Messaging | Message body text, attached multimedia files, timestamps, and delivery status. | 90 Days from delivery (or immediate administrative deletion). | Purged from real-time queues and active SMS message stores. |
| Emergency E911 Logs | Registered dispatchable address history, test logs, and 911 call transmission records. | 3 Years (Mandated by Federal 911 service continuity regulations). | Archived in access-restricted regulatory compliance repositories. |
| A2P 10DLC Consent | Consumer opt-in logs, STOP opt-out records, and campaign brand vetting tokens. | 4 Years (TCPA statute of limitations and CTIA carrier audit compliance). | Maintained in immutable compliance ledger for carrier verification. |
| Financial & Tax Records | Invoices, credit card transaction tokens, tax filings, and remittance receipts. | 7 Years (Federal and State statutory tax accounting requirement). | Stored in air-gapped financial archival databases; zero operational access. |
What Happens When Your Account Is Deleted
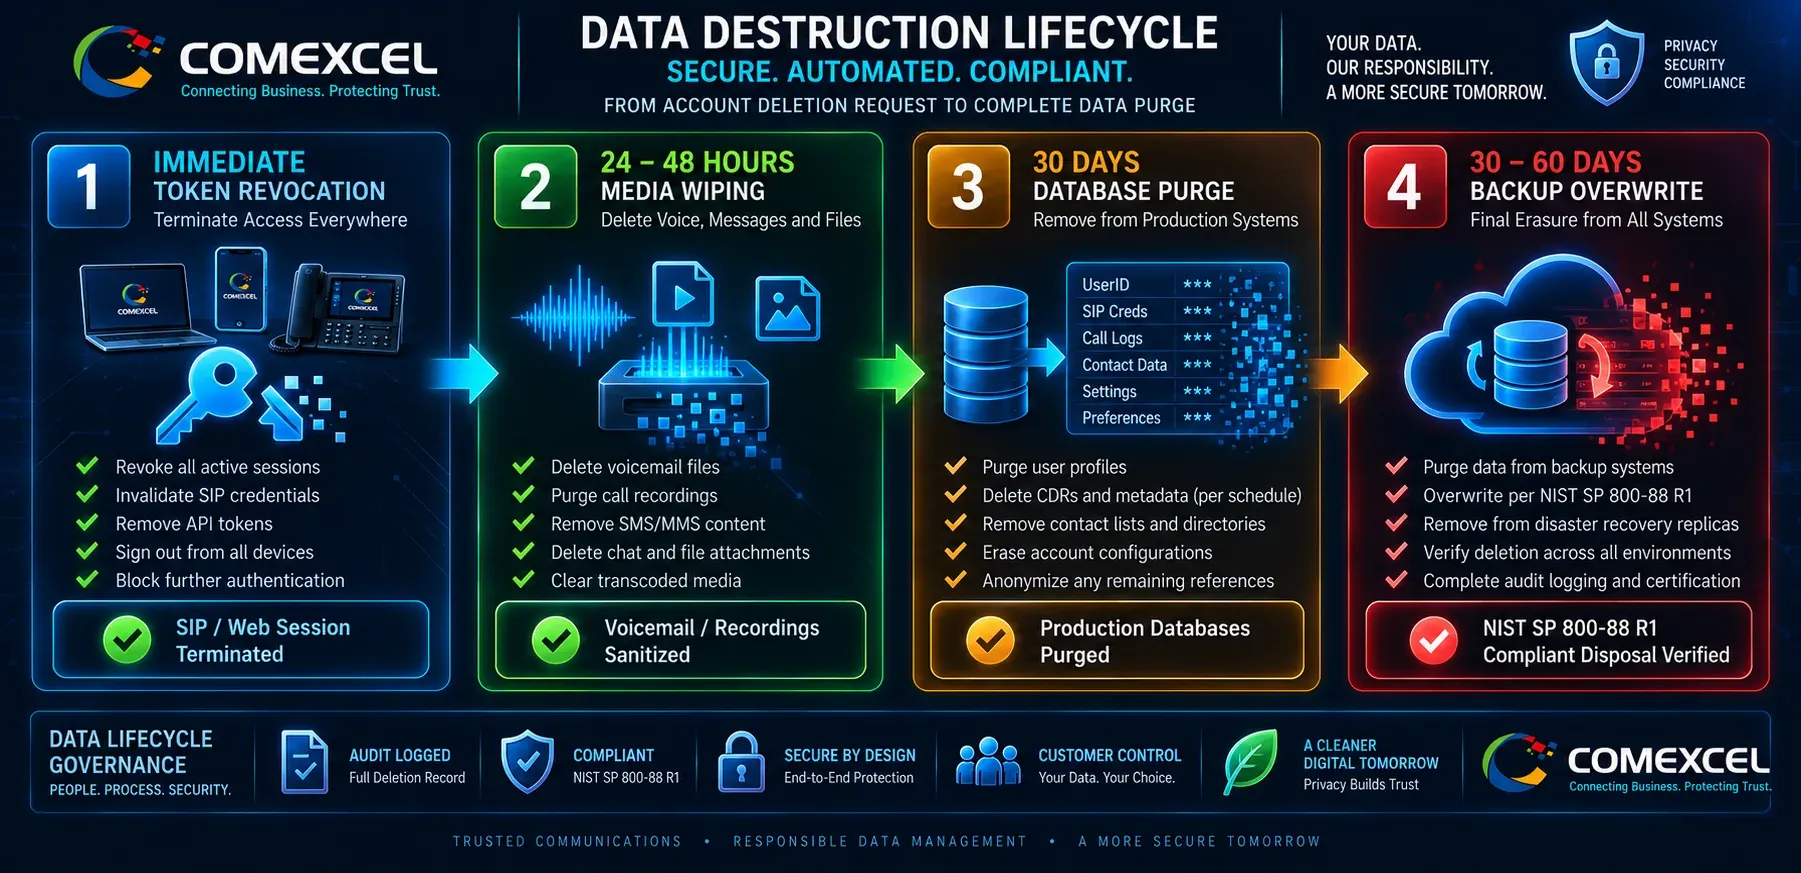
When an account owner or authorized administrator confirms account deletion, COMEXCEL executes a multi-stage data destruction pipeline:
| Stage | Purge Phase | Execution Timeline | Actions & Data Purged |
|---|---|---|---|
| Phase 1 | Immediate Suspension & Token Revocation | Instant (Upon Confirmation) | • Terminate active SIP endpoints, softphone tokens, and active web sessions.• Revoke “Sign in with Apple” and Google SSO authentication tokens. |
| Phase 2 | Media & Ephemeral Data Destruction | Within 24–48 Hours | • Permanently delete all voicemails, custom greetings, and call recordings.• Erase softphone contact books and locally cached SMS media. |
| Phase 3 | Multi-Tenant Database Purge | Within 30 Days | • Wipe user records, SIP credentials, and extension routing tables.• Disconnect downstream carrier routes and subprocessor API integrations. |
| Phase 4 | Encrypted Backup & Storage Overwrite | Within 30–60 Days | • Naturally overwrite and cycle out rotational system snapshots.• Apply NIST SP 800-88 R1 compliant cryptographic key destruction. |
- Deactivation vs. Deletion: COMEXCEL distinguishes between disabling an account and deleting it. Selecting account deletion triggers a permanent, irreversible purge across all active production environments.
- Apple & Third-Party SSO Token Revocation: If you authenticate via Sign in with Apple or Google SSO, submitting an account deletion request triggers a programmatic call to third-party identity providers to invalidate and revoke access tokens.
Statutory & Regulatory Retention Exceptions
Under applicable federal telecommunications laws, state accounting rules, and security frameworks, COMEXCEL is legally restricted from deleting certain records immediately upon account termination:
- Tax & Statutory Accounting: Invoices, payments, and business entity records are retained for seven (7) years to satisfy federal and state tax audits.
- Fraud Prevention & Network Integrity: Identifiers associated with verified illegal telemarketing, STIR/SHAKEN spoofing, or fraudulent traffic pumping are retained in internal security blacklists to protect network infrastructure.
- Litigation Holds & Subpoenas: If an account is subject to an active court order, lawful interception warrant, or pending legal dispute, deletion is temporarily suspended until formal legal release.
- FCC Emergency Regulations: Emergency 911 call records and dispatchable address audit logs are preserved in accordance with federal public safety rules.
- User Privacy Rights: For information on exercising statutory deletion rights outside of telecommunications regulatory holds, review the COMEXCEL Privacy Policy.
Subprocessor & Downstream Data Destruction
COMEXCEL ensures that your deletion requests cascade to all authorized third-party vendors and Tier-1 infrastructure providers:
| Media Storage Type | Physical / Logical Infrastructure | NIST SP 800-88 R1 Sanitization Method | Verification Standard |
|---|---|---|---|
| Active Relational DBs | Multi-tenant user tables, SIP routing directories | Logical Clear: Cryptographic key zeroing and multi-pass sector wiping | Automated deletion logs & immutable audit ledger |
| Object Media Stores | Voicemail audio, call recordings, call transcripts | Cryptographic Erase (CE): Multi-pass shredding of AES-256 file keys | Zero-byte block verification across SSD storage |
| Rotational Backups | Encrypted snapshots, off-site disaster archives | Purge via Natural Invalidation: 30–60 day rotational snapshot overwrite | Key expiration prevents post-purge decryption |
- Data Center Infrastructure: Storage volumes hosted within SOC 2 Type II data centers undergo multi-pass data sanitization according to NIST SP 800-88 R1 specifications.
- Upstream Carrier Aggregators: Deprovisioning commands are transmitted to upstream telecommunications partners to release phone numbers and remove brand routing tables.
- Campaign Registry (TCR): Associated 10DLC messaging campaigns are deactivated and unlinked from your entity identity.
Data Retention & Account Deletion Frequently Asked Questions (FAQs)
Can I recover my call recordings or voicemails after deleting my account?
No. Account deletion is permanent and irreversible. All stored audio files, voicemails, and call logs are permanently unlinked and destroyed. You must export necessary audio files before confirming account deletion.
Does deleting the mobile app from my iPhone or Android device delete my account?
No. Deleting or uninstalling the mobile app only removes local cached files from your physical handset. To delete your cloud account and server-side data, use the in-app deletion button before uninstalling, or submit a request via our web portal.
How long does it take for my data to be completely erased from backup systems?
Production databases are purged within 30 days. Full encrypted backup snapshots rotate out and are permanently overwritten within 30 to 60 days following the deletion request.
How does COMEXCEL dispose of healthcare ePHI under HIPAA?
For healthcare clients operating under a Business Associate Agreement (BAA), all electronic media containing ePHI is sanitized using cryptographic erasure and NIST SP 800-88 R1 media disposal protocols in full accordance with our HIPAA Compliance & Security Statement.
Data Privacy & Account Deletion Helpdesk
Need assistance with account deletion, data extraction, or statutory erasure requests? Our data governance and privacy teams process all GDPR, CCPA, and App Store erasure requests in accordance with strict statutory verification standards.