Effective Date: September 10, 2026 | Last Updated: September 10, 2026
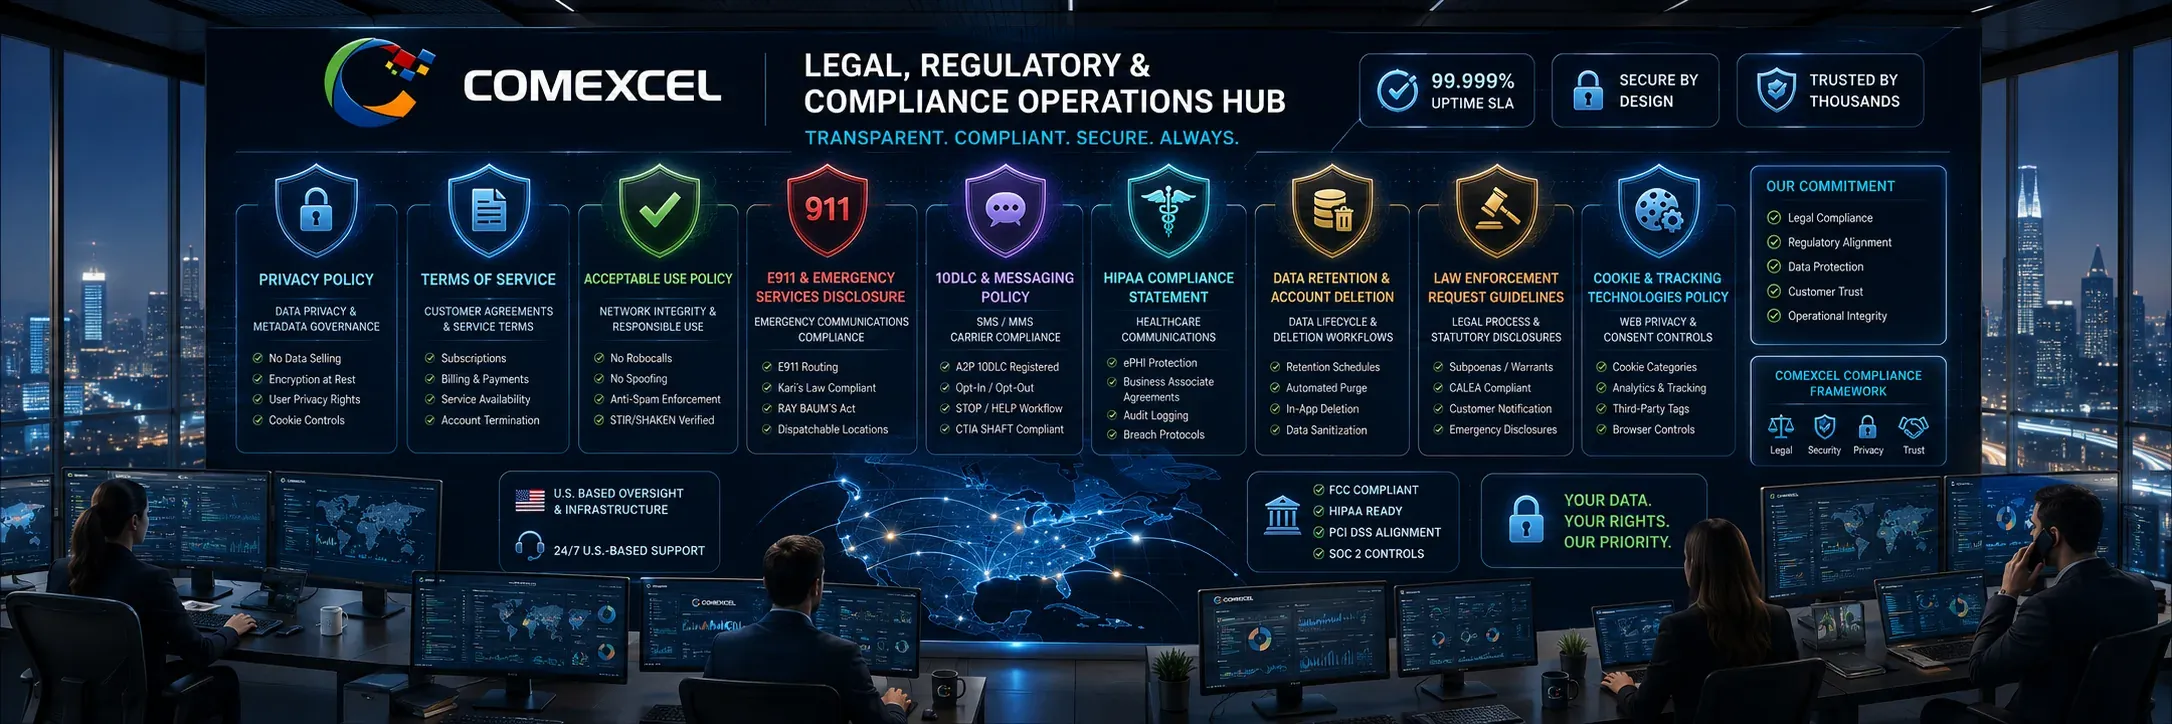
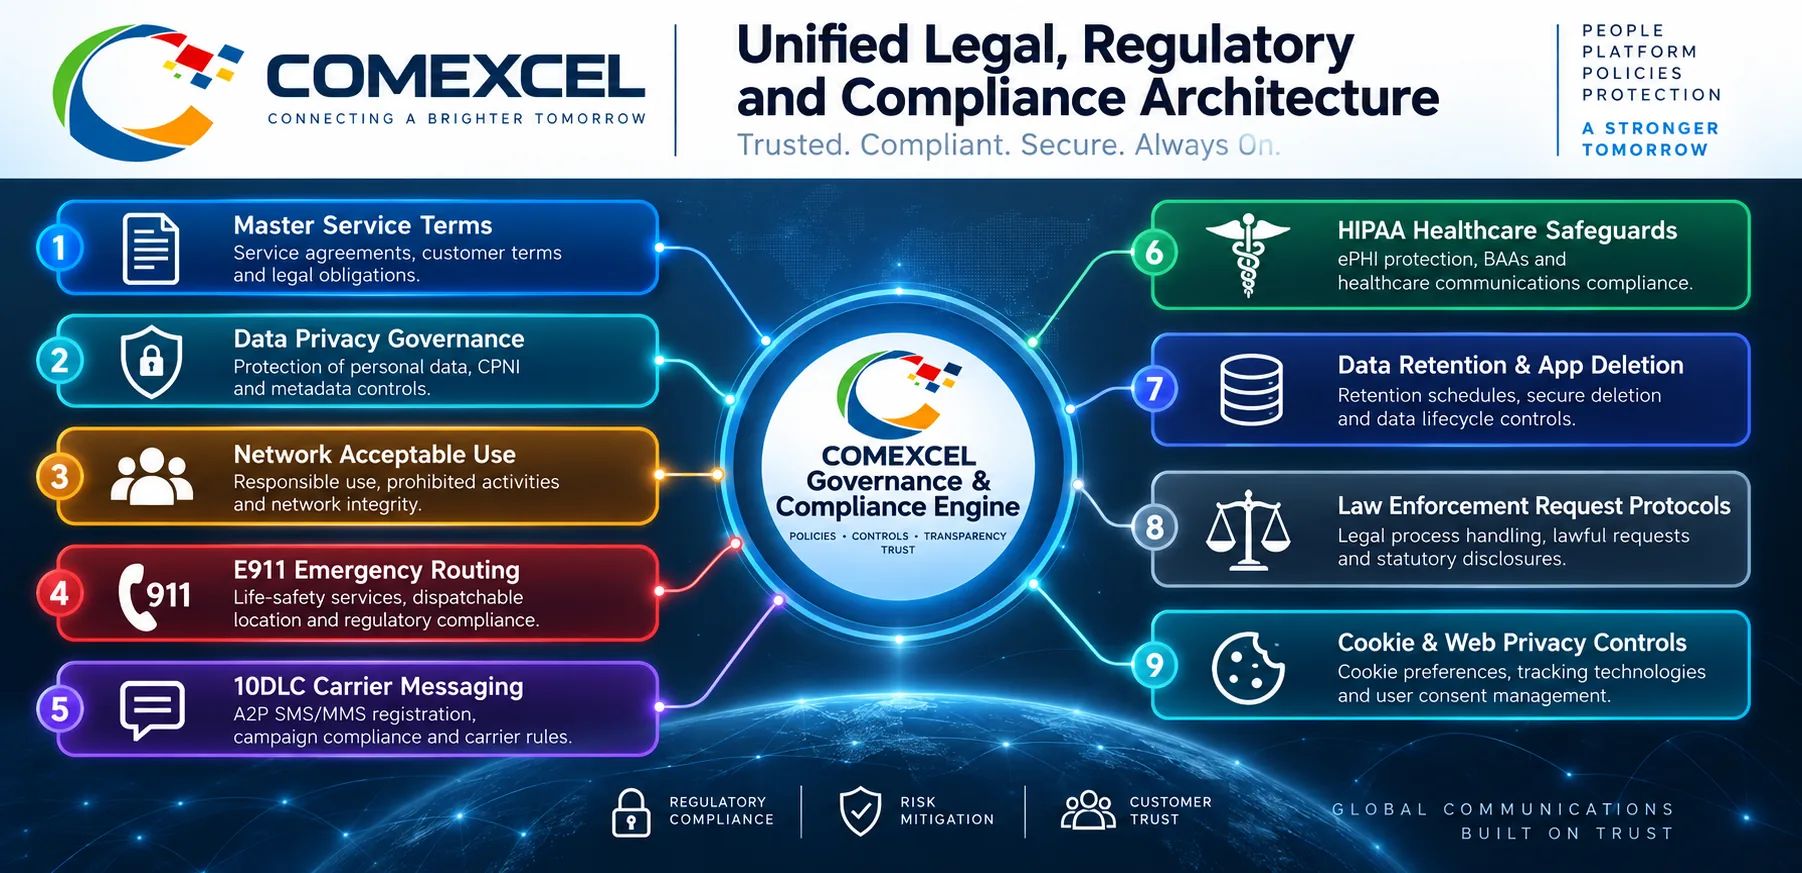
COMEXCEL Legal, Regulatory & Compliance Center establishes the contractual agreements, regulatory disclosures, network integrity rules, and data governance frameworks that govern our complete cloud communications suite. COMEXCEL provides enterprise-grade infrastructure across our Business VoIP & Cloud PBX Solutions, business SMS/MMS messaging, mobile endpoints, and regulated healthcare communications. Whether you are an IT administrator configuring multi-site routing, a healthcare privacy officer evaluating statutory safeguards, or an enterprise procurement director conducting vendor due diligence, this repository outlines binding operating standards designed to ensure lawful, resilient, and transparent telecommunications.
Legal & Regulatory Framework at a Glance
- Comprehensive Customer Governance: Legally binding service agreements, acceptable use standards, and transparent data privacy practices.
- User Data Lifecycle & App Store Compliance: Clear data retention schedules, automated media purging, and self-service account deletion workflows compliant with Apple App Store and Google Play standards.
- Life Safety & Federal Mandates: Interconnected VoIP emergency calling architectures aligned with Kari’s Law and the RAY BAUM’S Act.
- 10DLC Messaging Standards: End-to-end messaging rules compliant with TCPA statutes, CTIA guidelines, and Tier-1 carrier campaign registries.
- Regulated Healthcare Safeguards: Administrative, physical, and technical safeguards engineered for HIPAA Security Rule compliance, including Business Associate Agreements (BAAs).
- Enterprise Due Diligence & Legal Process: Tamper-evident audit trails, transparent cookie tracking controls, and formal law enforcement request validation protocols.
Core Policies & Customer Agreements
Core Service Agreements & Customer Terms
Review the master contractual agreements, data privacy governance, and responsible use policies that establish the baseline operational standards for all COMEXCEL subscriptions and accounts.
Privacy Policy
Privacy & Data GovernanceUnderstand how COMEXCEL collects, uses, protects, and manages customer account information, communications metadata, and website visitor data without selling personal records.Key Topics: Data collection, account credentials, metadata, cookies, information sharing restrictions, and privacy rights.Read Privacy Policy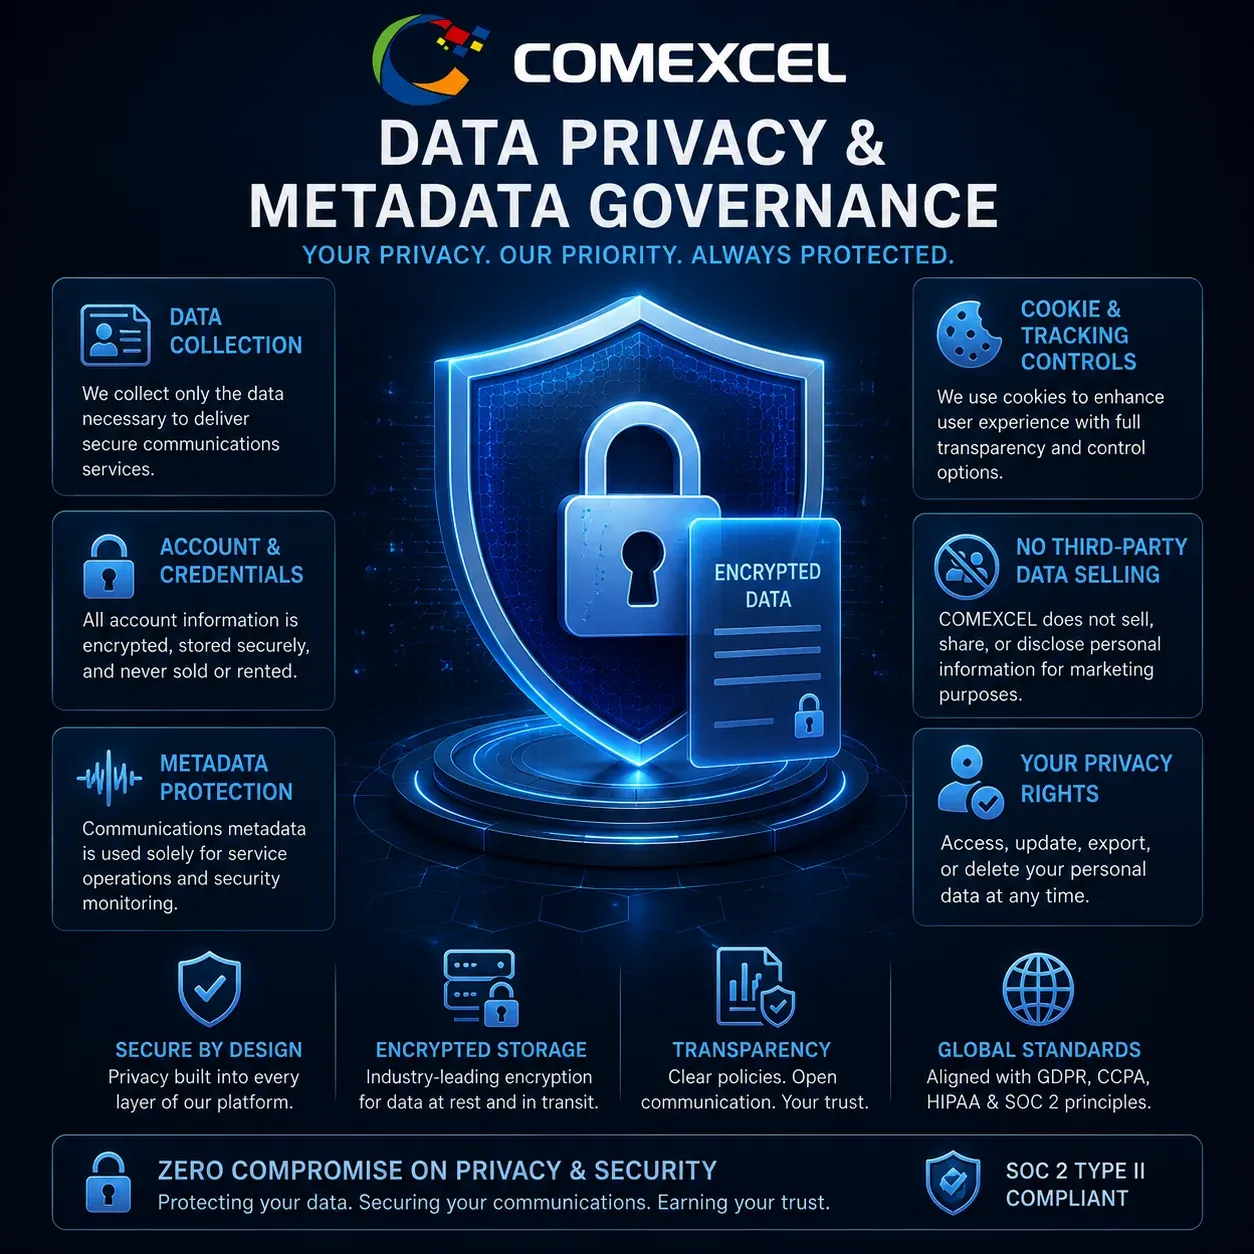
Terms of Service
Customer Agreement & Service TermsReview the contractual terms governing COMEXCEL subscriptions, account administration, billing schedules, payment terms, service availability, and operational responsibilities.Key Topics: Subscriptions, billing cycles, user access management, service uptime, dispute resolution, and account termination.Review Terms of Service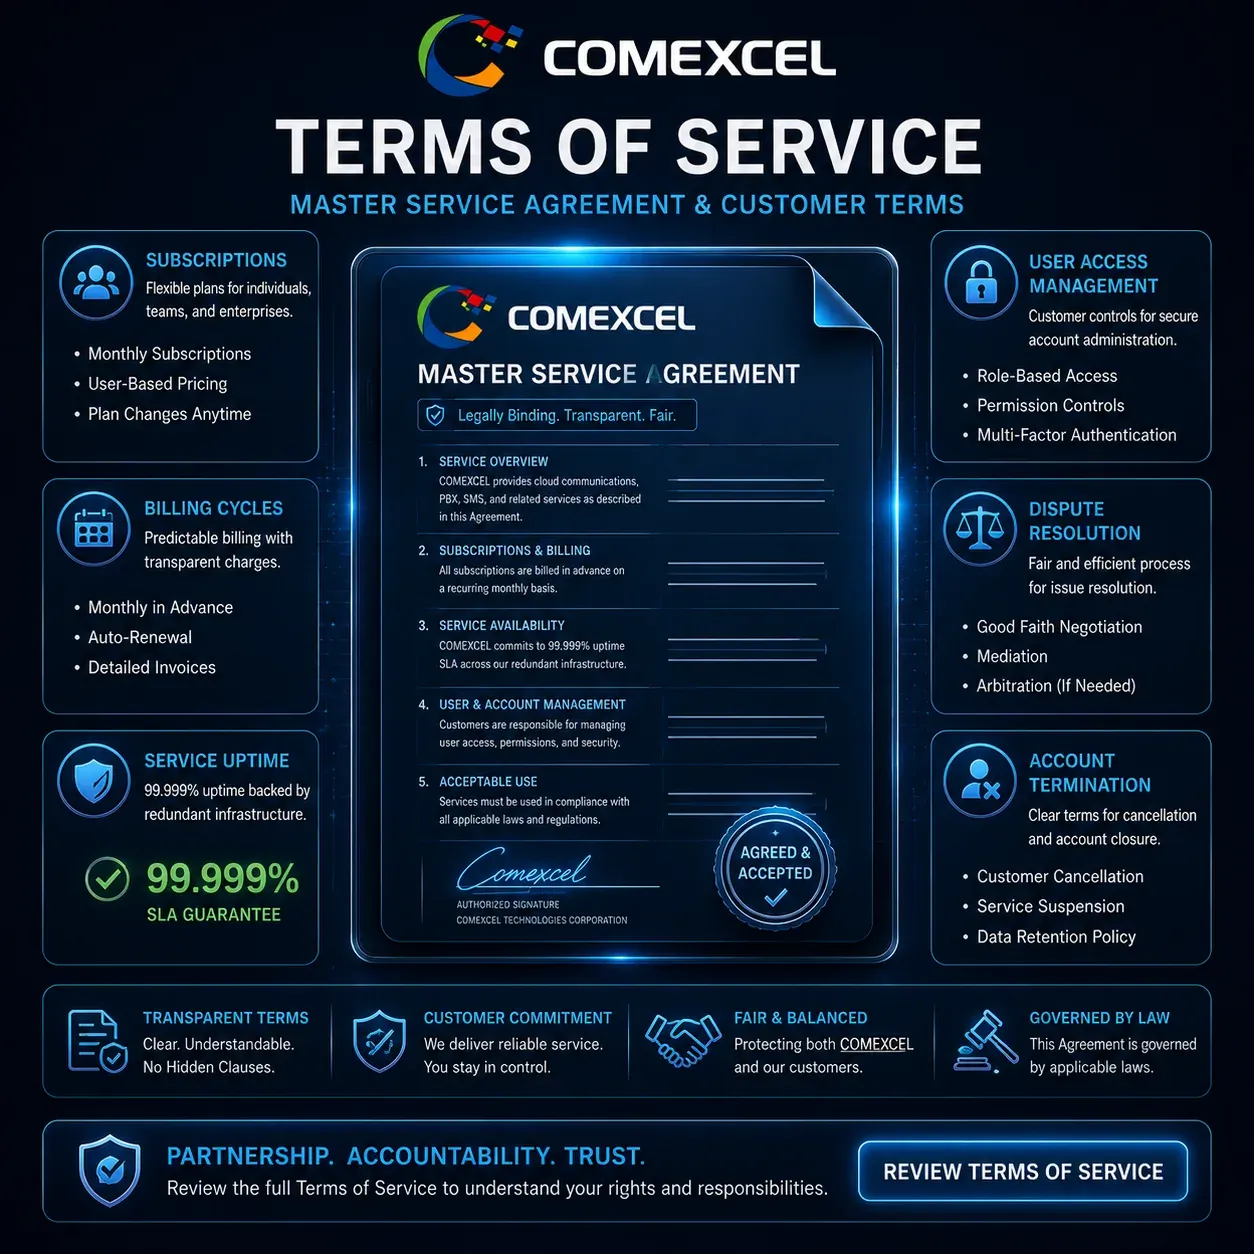
Acceptable Use Policy
Network Integrity & Responsible UseLearn the operational standards governing voice, messaging, and API services, including strict bans on robocalling, caller ID spoofing, fraudulent traffic, and network abuse.Key Topics: Prohibited traffic, anti-spam rules, auto-dialer limits, STIR/SHAKEN verification, and network security enforcement.View Acceptable Use Policy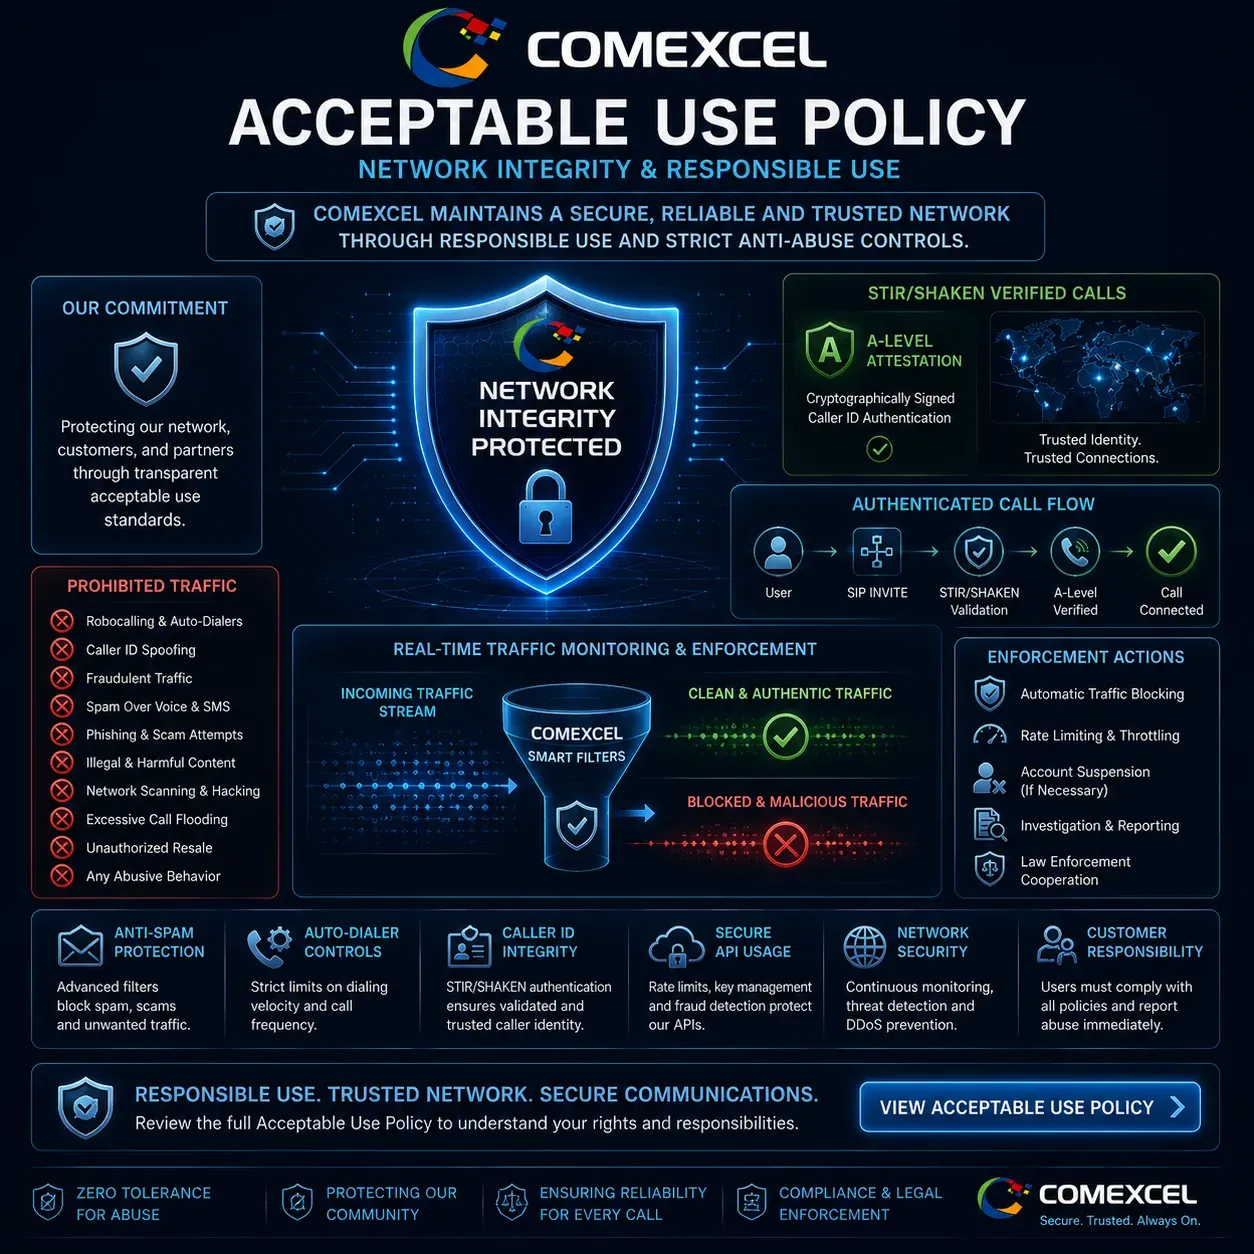
Regulatory, Safety & Compliance Policies
Regulatory Disclosures, Safety & Industry Compliance
Access specialized regulatory frameworks governing emergency 911 life-safety communications, carrier-grade 10DLC text messaging registration, and HIPAA healthcare data safeguards.
E911 & Emergency Services Disclosure
Emergency CommunicationsUnderstand how 911 dialing operates across cloud VoIP, including dispatchable location obligations, nomadic remote worker configurations, and power outage procedures.Key Topics: E911 routing, registered locations, Kari’s Law direct dialing, RAY BAUM’S Act, softphones, and emergency notifications.Review E911 Disclosure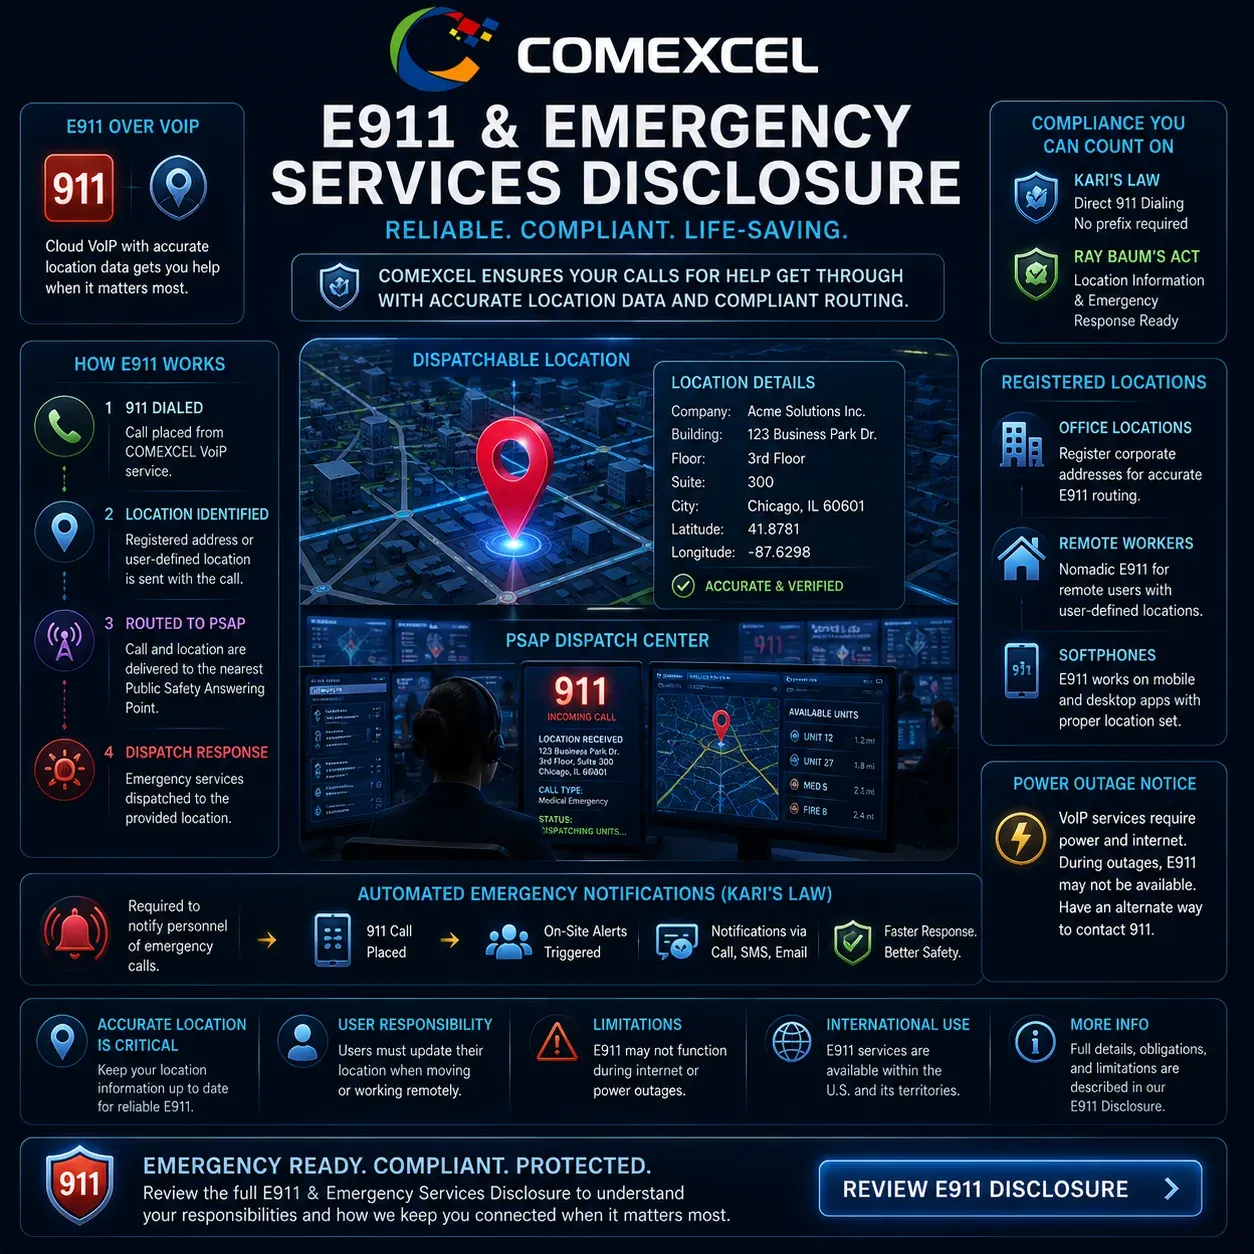
10DLC & Messaging Policy
SMS / MMS ComplianceReview mandatory standards for business text messaging, including TCR campaign vetting, verified opt-in consent, automated opt-out keywords, and CTIA SHAFT bans.Key Topics: A2P 10DLC registration, consent records, STOP/HELP workflows, throughput limits, and carrier surcharge enforcement.Review Messaging Policy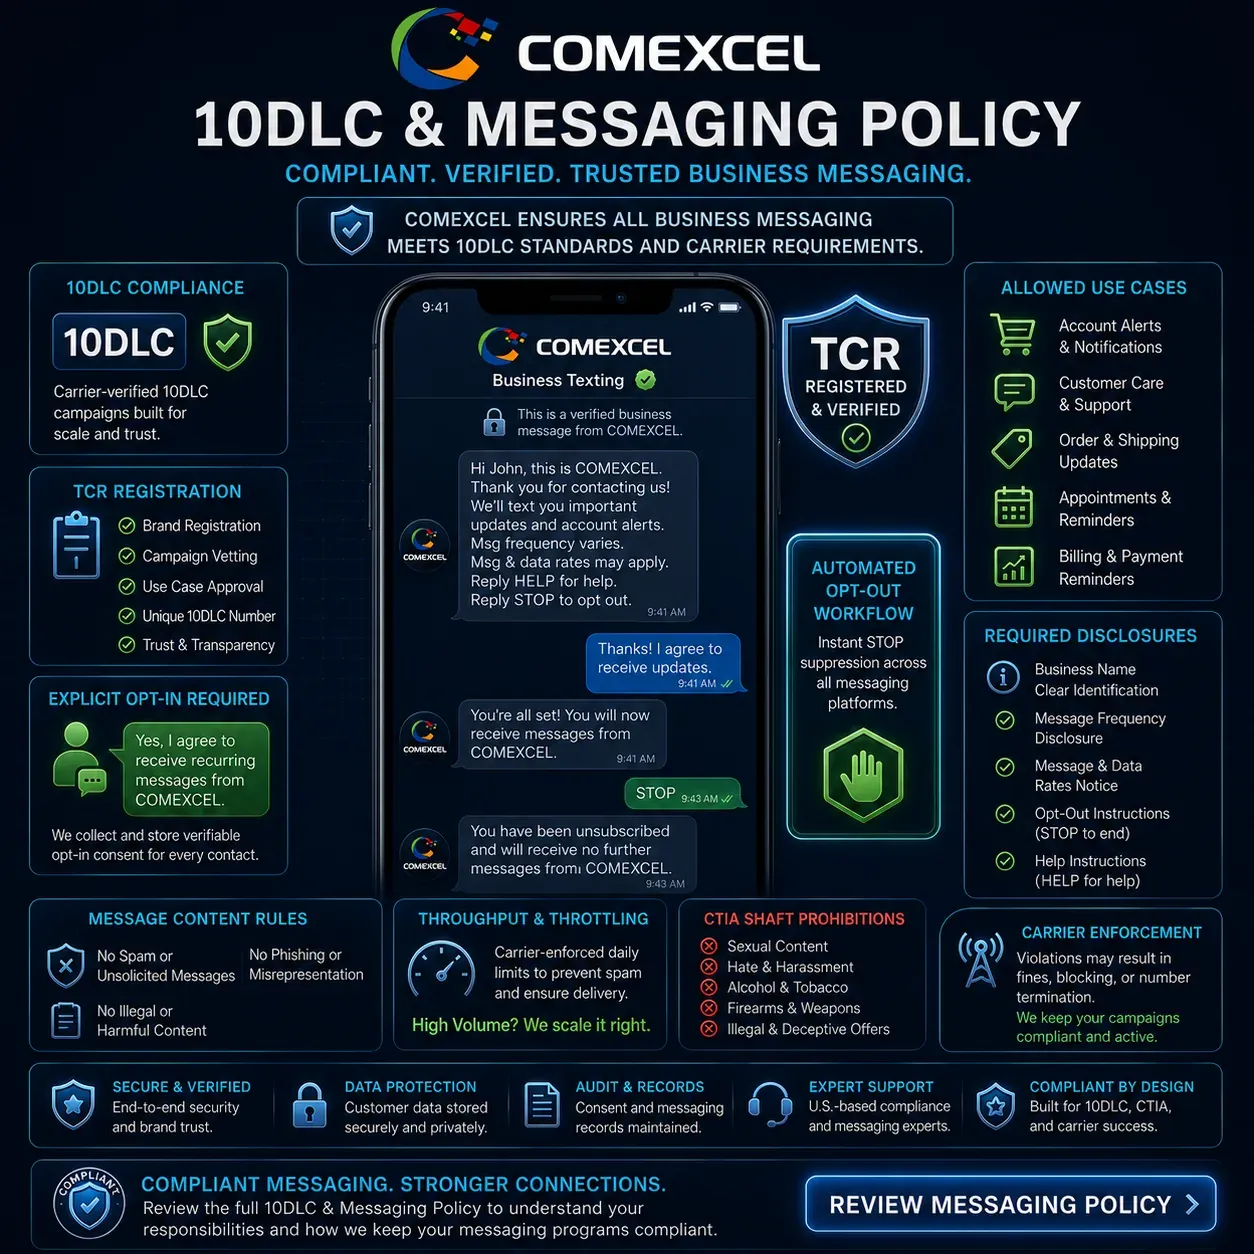
HIPAA Compliance Statement
Healthcare CommunicationsLearn how COMEXCEL safeguards electronic Protected Health Information (ePHI) with TLS 1.3/SRTP encryption, audit logging, role-based access, and signed BAAs.Key Topics: ePHI protection, Business Associate Agreements (BAAs), encrypted call recording, access controls, and breach protocols.Explore HIPAA Compliance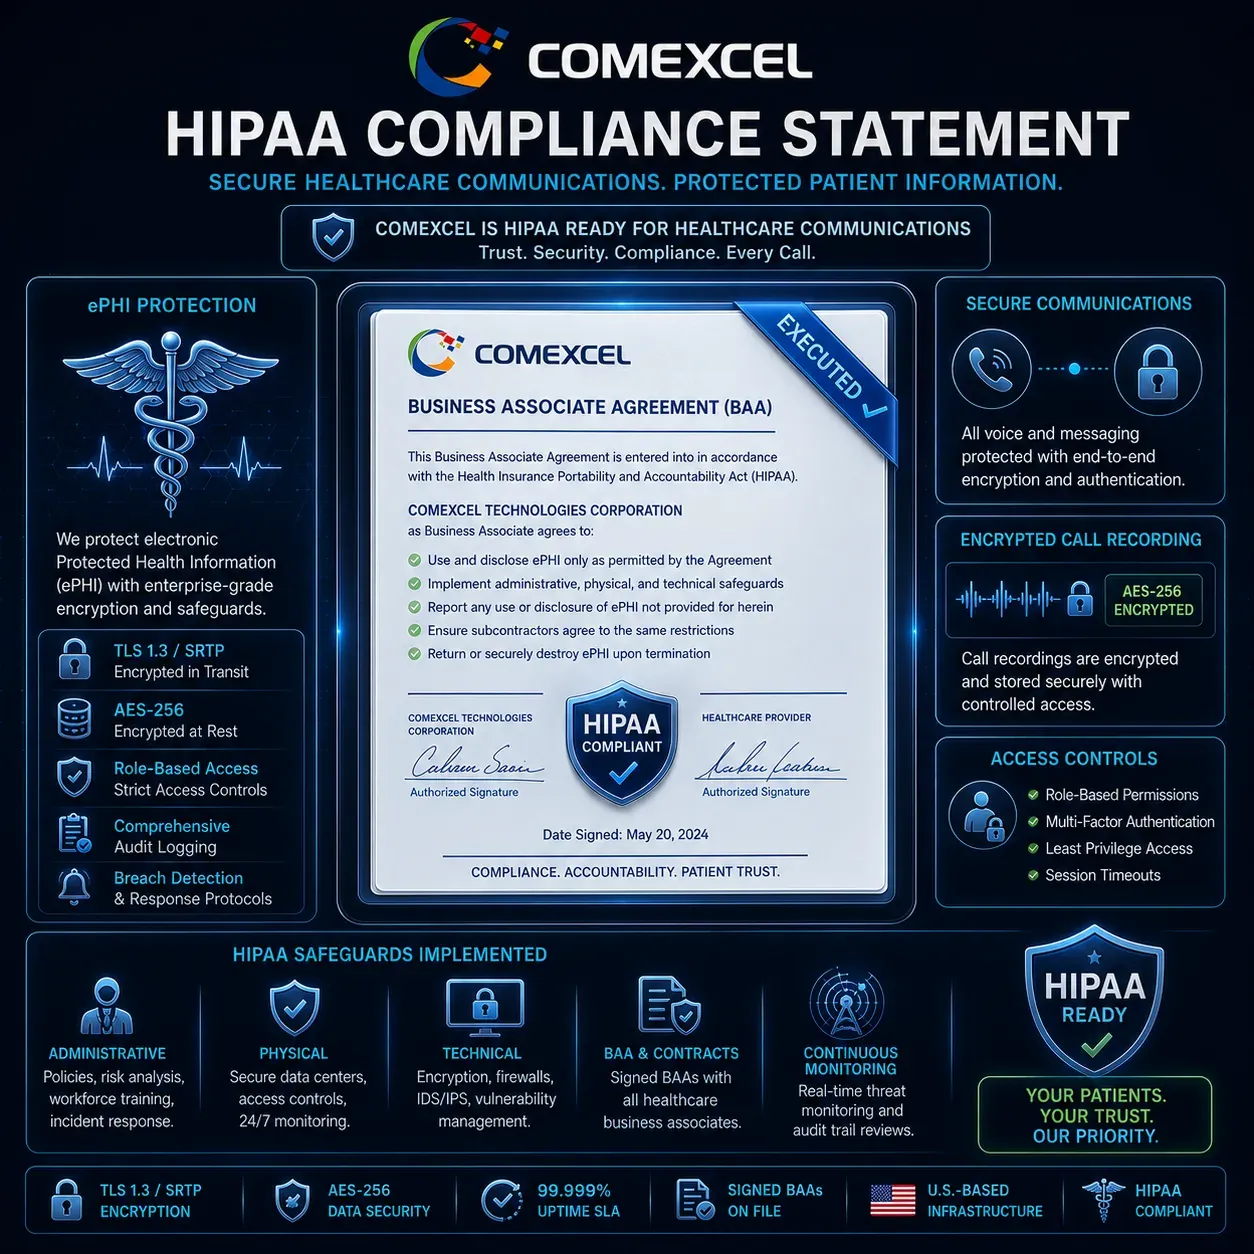
Data Governance, Tracking & Legal Process Policies
Data Lifecycle, Web Privacy & Statutory Request Protocols
Manage customer data lifecycles, review user deletion mechanisms for mobile and cloud applications, understand cookie tracking controls, and inspect official protocols for statutory law enforcement inquiries.
Data Retention & Account Deletion Policy
Data Lifecycle & App Store ComplianceReview retention timetables, automated media purge cycles, and end-user self-service deletion workflows required for COMEXCEL mobile apps on the Apple App Store and Google Play.Key Topics: Retention timetables, call detail record (CDR) lifecycles, account deprovisioning, in-app deletion workflows, and cryptographic data sanitization.Review Retention & Deletion Policy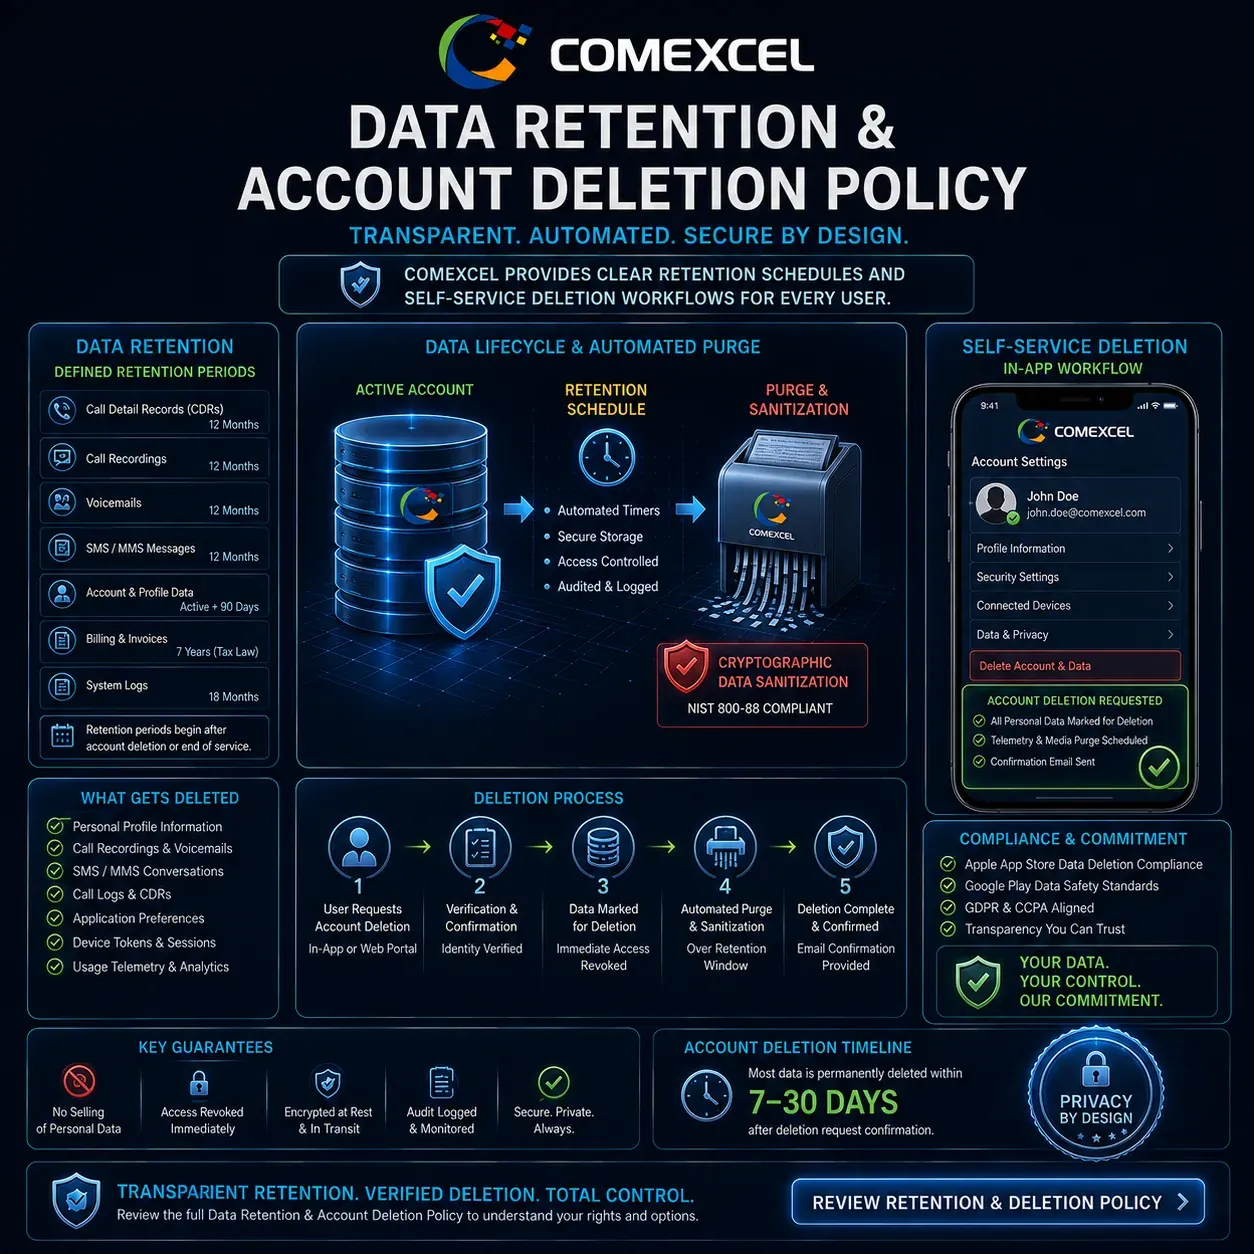
Law Enforcement Request Guidelines
Legal Process & Statutory DisclosuresUnderstand our standards and requirements for processing subpoenas, court orders, search warrants, CALEA requests, and emergency data access notices from government agencies.Key Topics: Legal process verification, CALEA compliance, customer notification rules, emergency disclosures, and law enforcement contact protocols.View Law Enforcement Guidelines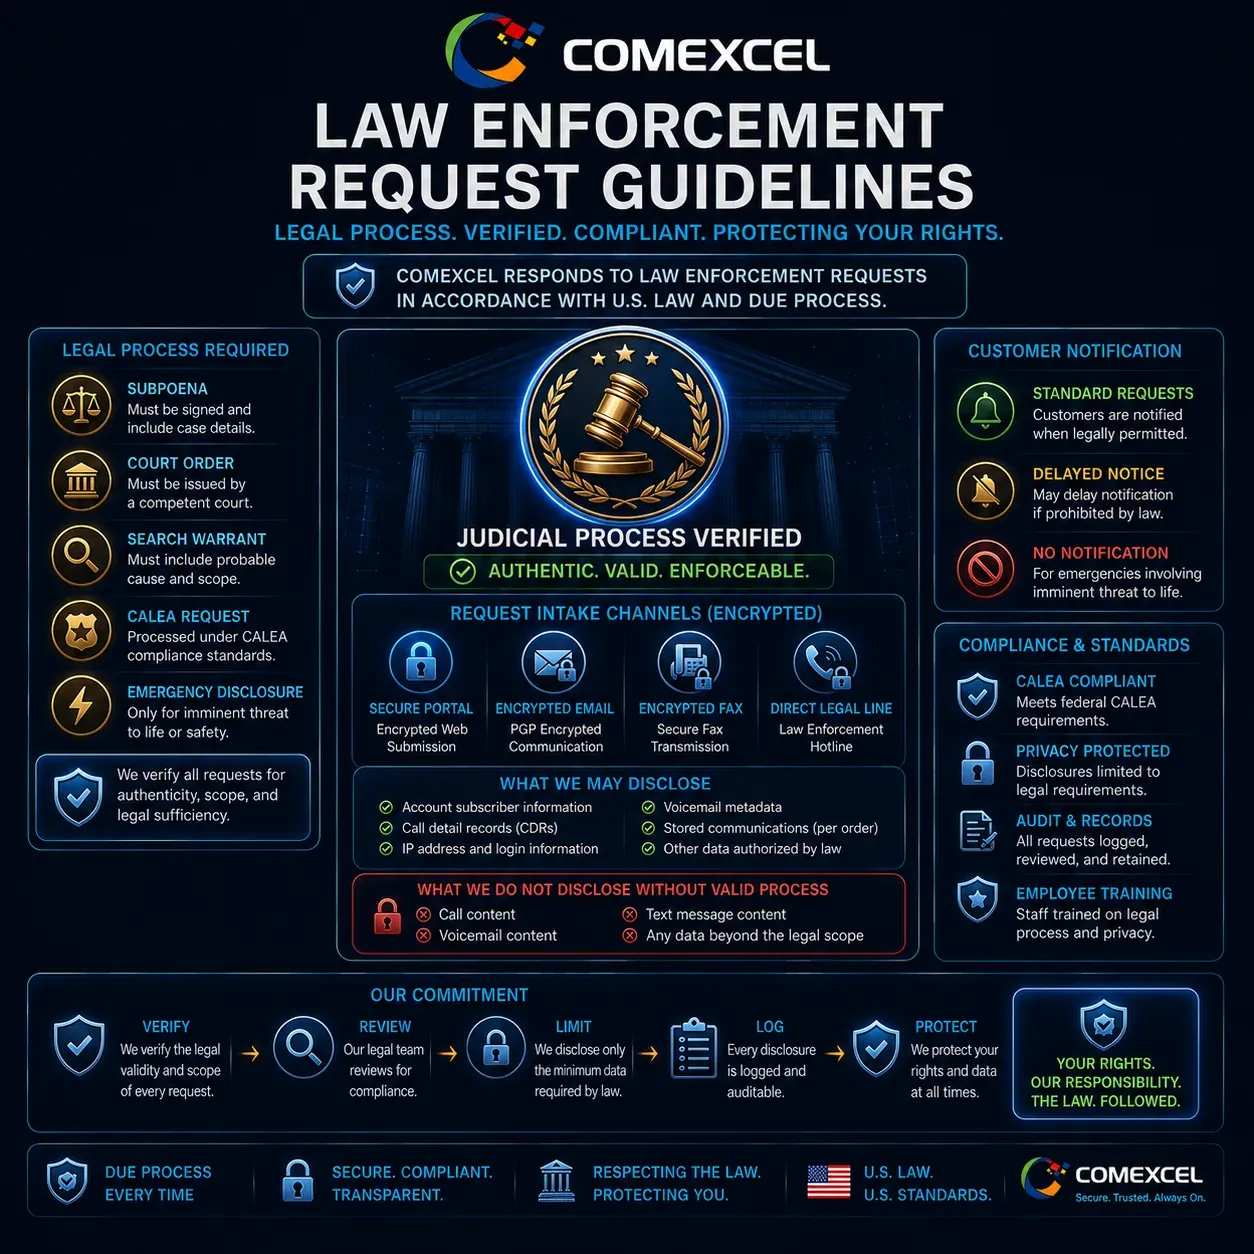
Cookie & Tracking Technologies Policy
Web Privacy & Consent ControlsLearn how COMEXCEL utilizes essential, functional, analytical, and performance cookies across our web properties, including instructions for managing browser consent preferences.Key Topics: Cookie categories, tracking technologies, analytics consent, third-party tags, and browser-level opt-out mechanisms.View Cookie Policy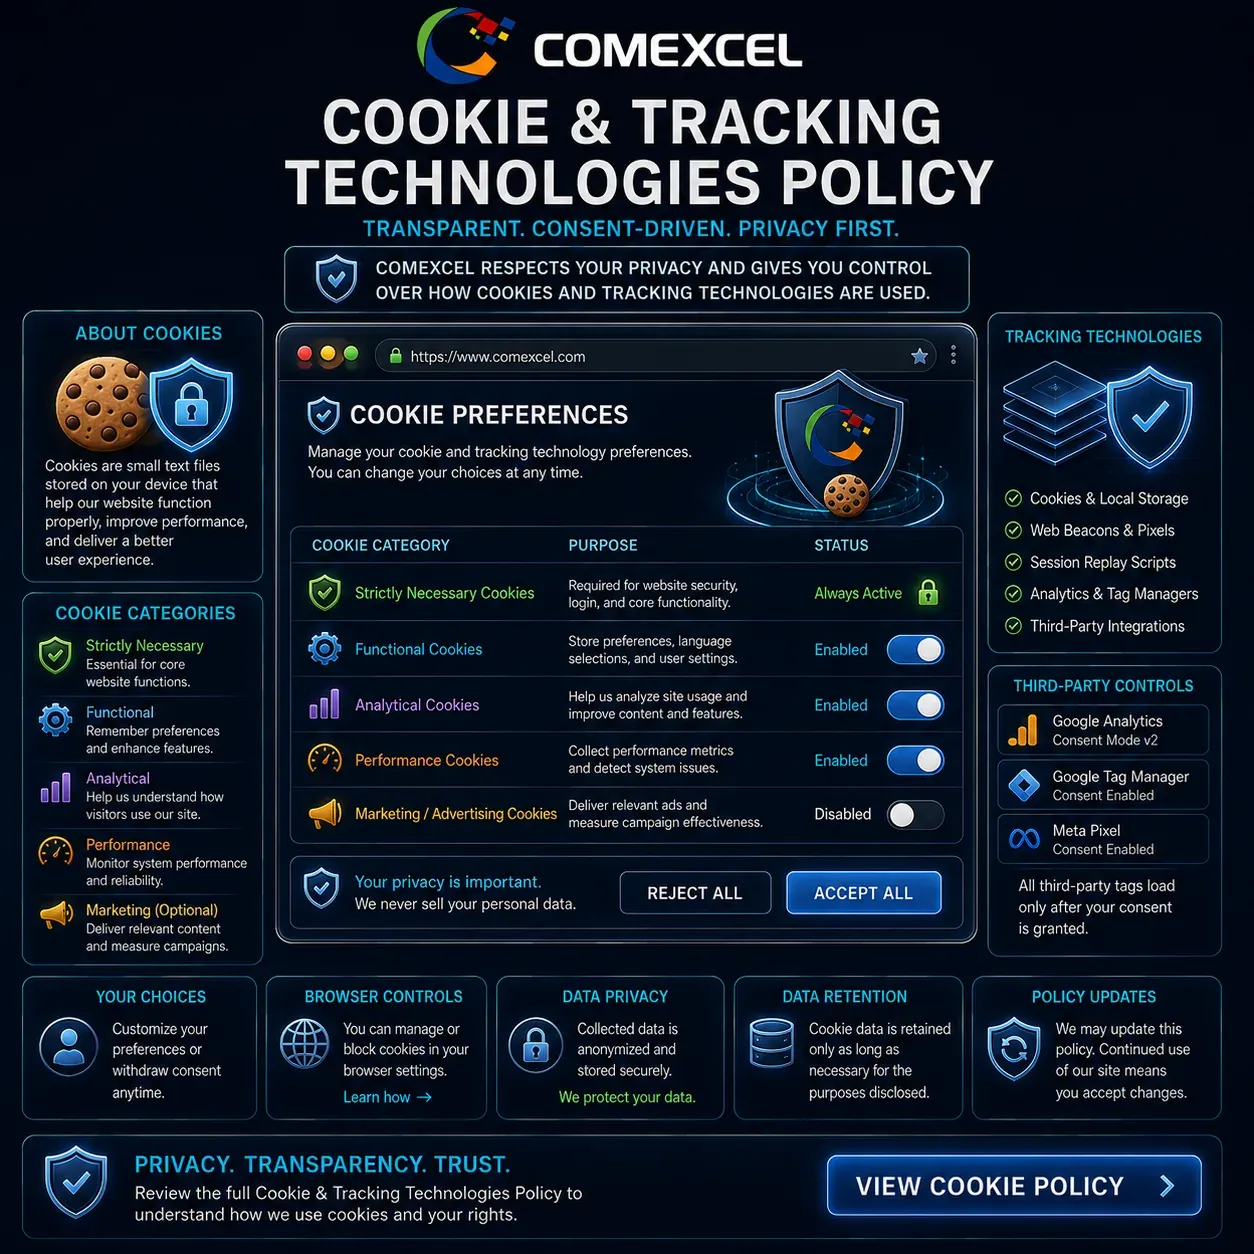
Compliance by Business Environment
Different operating models have unique legal and regulatory mandates. Alongside the physical and cryptographic infrastructure detailed in our Security & Trust Center, the matrix below highlights which statutory policies apply directly to your organization:
| Business Environment | Primary Regulatory Focus | Applicable COMEXCEL Documents | Key Compliance Action Required |
|---|---|---|---|
| Small Businesses | Commercial contracting, basic E911, and customer SMS consent. | Terms of Service, Privacy Policy, Messaging Policy | Maintain valid payment methods, capture SMS consent, and register primary office addresses. |
| Multi-Location Enterprises | Multi-site E911 routing, role-based provisioning, and call recording governance. | E911 Disclosure, Acceptable Use, Terms of Service | Assign dynamic dispatchable locations per endpoint and configure call recording IVR disclosures. |
| Mobile & App Store End Users | In-app account deletion, mobile permission audits, and local cache purge. | Data Retention & Deletion, Privacy Policy | Use in-app mobile settings or web console to initiate user deprovisioning and data purge requests. |
| Remote & Hybrid Workforces | Nomadic emergency calling, softphone data security, and access control. | E911 Disclosure, Privacy Policy, Acceptable Use | Mandate remote user address verification in softphone apps and enforce MFA on user accounts. |
| Healthcare & Medical Groups | ePHI confidentiality, encrypted media transport, and BAA execution. | HIPAA Compliance, Privacy Policy, Terms of Service | Execute a COMEXCEL BAA, verify TLS/SRTP voice encryption, and restrict call recording access. |
| Contact Centers & Sales Teams | TCPA compliance, 10DLC throughput, and automated opt-out enforcement. | Messaging Policy, Acceptable Use Policy | Register TCR messaging campaigns and synchronize real-time opt-out webhooks with internal CRMs. |
| IT, SecOps & Legal Process | API security, statutory subpoena handling, web tracking, and data retention schedules. | Law Enforcement Guidelines, Data Retention Policy, Cookie Policy, Security Center | Configure organization-wide retention rules, manage cookie preferences, and route legal process to legal counsel. |
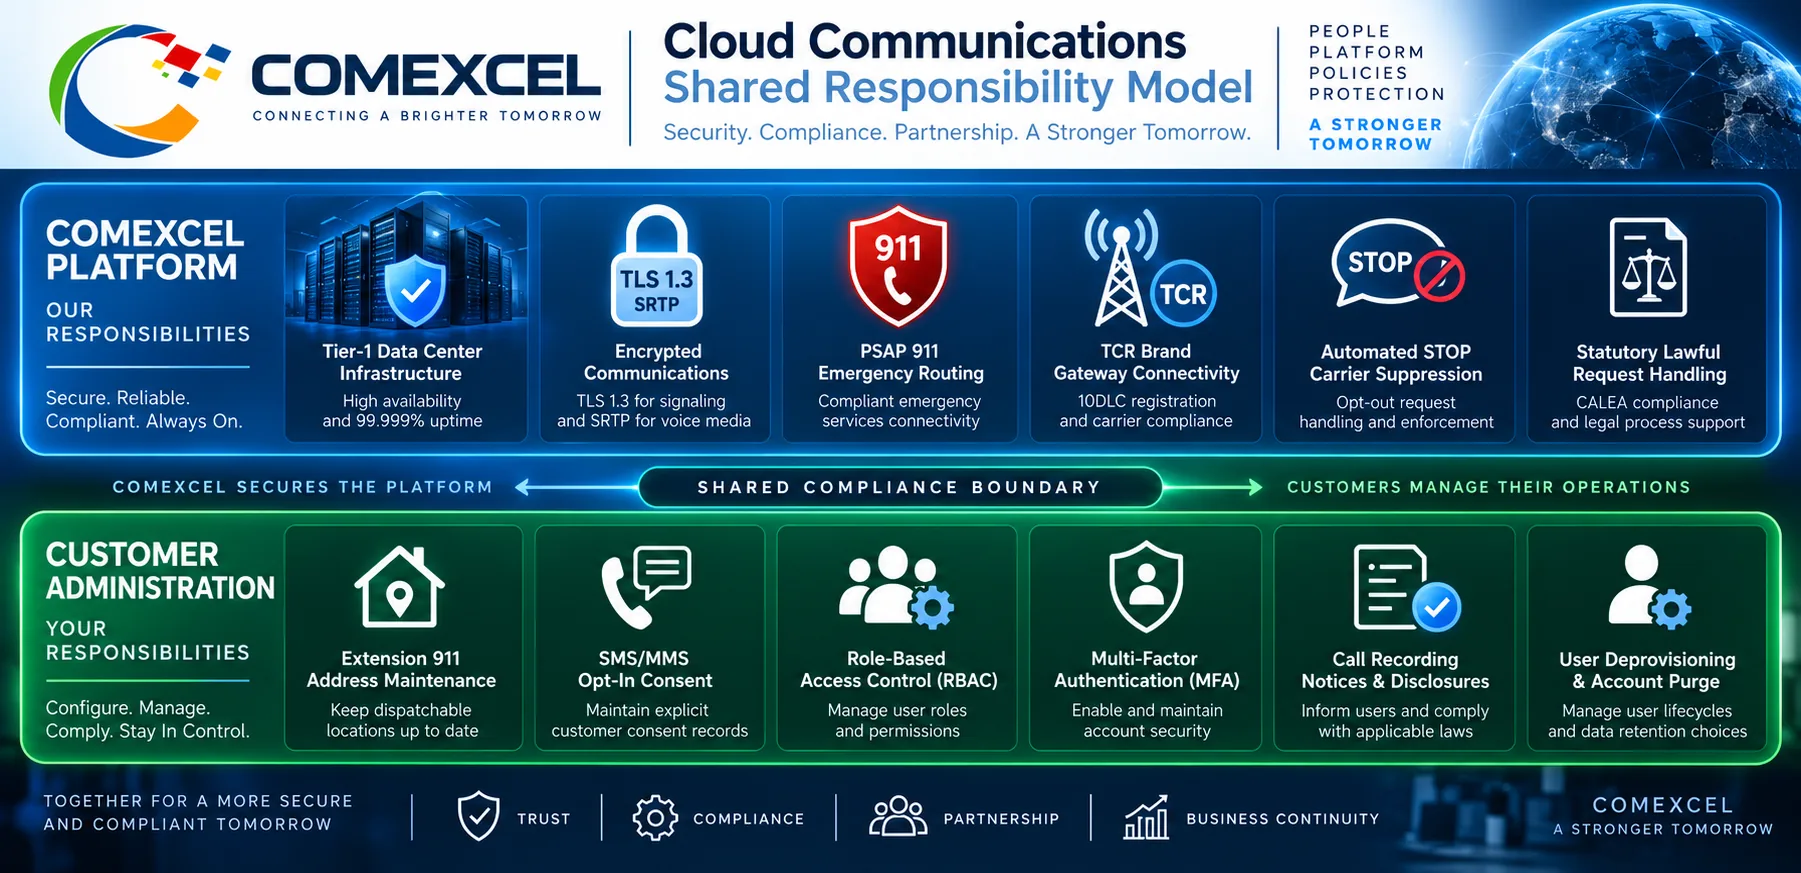
Shared Responsibility Model
Maintaining legal and regulatory compliance across cloud communications is a joint commitment between COMEXCEL and your organization:
| COMEXCEL Platform Responsibilities | Customer Operational Responsibilities |
|---|---|
| Secure, geo-redundant Tier-1 data center and cloud switching infrastructure | Maintaining accurate registered dispatchable addresses for all user extensions |
| End-to-end cryptographic signaling (TLS 1.3) and media encryption (SRTP) | Obtaining explicit prior consent from consumers prior to sending SMS/MMS |
| E911 emergency call routing integration with national Public Safety Gateways | Enforcing strong user credentials, role-based permissions, and MFA |
| Direct connectivity with The Campaign Registry (TCR) for 10DLC brand vetting | Complying with federal and state call recording notification requirements |
| Automated system-level opt-out suppression (STOP/HELP) at carrier gateways | Managing internal user account deprovisioning and data purge requests |
| Execution of formal Business Associate Agreements (BAAs) for healthcare | Configuring system integrations to prevent unauthorized exposure of ePHI |
| Statutory compliance with CALEA and validated law enforcement court orders | Operating in full compliance with TCPA, TSR, CTIA, and local statutes |
Policy Decision Matrix: Which Document Do You Need?
| If your inquiry involves… | Governing Policy & Access |
|---|---|
| How personal and business account data is collected, stored, and protected | Privacy Policy |
| Billing terms, subscription cycles, account administration, and service limitations | Terms of Service |
| Prohibited calling practices, auto-dialer boundaries, and anti-spam enforcement | Acceptable Use Policy |
| Deleting mobile app accounts, purging CDR logs, or inspecting data retention timetables | Data Retention & Account Deletion Policy |
| 911 emergency dialing, remote worker addresses, and Kari’s Law / RAY BAUM’S Act rules | E911 & Emergency Disclosure |
| Business SMS/MMS consent, 10DLC campaign registration, and STOP opt-out handling | 10DLC & Messaging Policy |
| Healthcare ePHI protection, encrypted voice streams, call recording, and signed BAAs | HIPAA Compliance Statement |
| Government subpoenas, legal process validation, and statutory CALEA orders | Law Enforcement Request Guidelines |
| Website cookies, performance analytics tags, and tracking consent management | Cookie & Tracking Technologies Policy |
| Platform architecture, physical data center security, and technical cipher suites | Security & Trust Center |
Document Governance & Version Control
COMEXCEL maintains formal document lifecycle governance. All active legal and regulatory policies are indexed with current effective dates below:
| Document Title | Document Type | Version Status | Effective Date | Direct Access Link |
|---|---|---|---|---|
| Privacy Policy | Data Governance | Active (v2026.2) | September 10, 2026 | View Policy |
| Terms of Service | Master Agreement | Active (v2026.2) | September 10, 2026 | View Terms |
| Acceptable Use Policy | Network Standards | Active (v2026.2) | September 10, 2026 | View Policy |
| Data Retention & Deletion Policy | User Lifecycle | Active (v2026.2) | September 10, 2026 | View Policy |
| E911 Disclosure | Regulatory / Safety | Active (v2026.2) | September 10, 2026 | View Disclosure |
| 10DLC & Messaging Policy | Carrier Compliance | Active (v2026.2) | September 10, 2026 | View Policy |
| HIPAA Compliance Statement | Healthcare Security | Active (v2026.2) | September 10, 2026 | View Statement |
| Law Enforcement Guidelines | Legal Process | Active (v2026.2) | September 10, 2026 | View Guidelines |
| Cookie & Tracking Policy | Web Privacy | Active (v2026.2) | September 10, 2026 | View Policy |
Legal & Compliance Frequently Asked Questions (FAQ)
Where can I find COMEXCEL’s complete legal policies?
All formal customer contracts, regulatory disclosures, network use policies, data lifecycle rules, and carrier compliance statements are centrally published and maintained on this Legal Hub. Technical architecture and infrastructure safeguards can be accessed in our Security & Trust Center.
How do I request account deletion or data removal for the COMEXCEL mobile app?
Users on iOS and Android can initiate an account deletion request directly inside the COMEXCEL application under Account Settings or through our web portal. Full timelines and data purging standards are documented in our Data Retention & Account Deletion Policy.
How long does COMEXCEL retain call recordings, voicemail, and SMS logs?
Customer data retention varies by data type and account configuration. Standard call detail records (CDRs) and messages are stored according to regulatory requirements before automated cryptographic purging, as detailed in our Data Retention & Account Deletion Policy.
What primary agreement governs my COMEXCEL subscription?
All account subscriptions, billing terms, acceptable use requirements, and service level commitments are governed by the COMEXCEL Terms of Service alongside any applicable service orders.
How does COMEXCEL protect customer personal data and communications metadata?
We implement strict administrative, technical, and physical safeguards outlined in our Privacy Policy. COMEXCEL does not sell customer personal information, call records, or messaging logs to third parties.
How can website visitors manage cookie preferences?
Visitors can manage or withdraw consent for analytical and performance tracking tags at any time using our cookie preference center, detailed in our Cookie & Tracking Technologies Policy.
What activities are strictly prohibited across the COMEXCEL network?
Our Acceptable Use Policy strictly bans unlawful robocalling, unauthenticated caller ID spoofing, fraudulent traffic pumping, continuous auto-dialing without consent, phishing, and any activity that degrades network integrity.
How does 911 emergency calling work on COMEXCEL VoIP?
Emergency calls route over our interconnected VoIP network to local Public Safety Answering Points (PSAPs) using the user’s registered dispatchable address. Detailed setup instructions and nomadic worker rules are documented in our E911 Disclosure.
What are an employer’s responsibilities for remote worker E911 locations?
Under the RAY BAUM’S Act and COMEXCEL policy, account administrators and remote employees must update their registered physical address whenever they relocate their desktop IP phone or softphone app.
What is A2P 10DLC registration, and why is it required for SMS?
A2P 10DLC is the mobile carrier standard requiring businesses to register their brand identity and messaging use cases with The Campaign Registry (TCR) before sending text messages, as detailed in our 10DLC & Messaging Policy.
How does COMEXCEL handle subpoenas and government data requests?
COMEXCEL strictly complies with valid legal processes, including court orders, subpoenas, and CALEA warrants. All statutory protocols and emergency submission procedures are outlined in our Law Enforcement Request Guidelines.
How does COMEXCEL support HIPAA-regulated healthcare organizations?
We provide encrypted voice channels (TLS 1.3/SRTP), AES-256 encrypted media repositories, immutable audit logs, and execute standard Business Associate Agreements (BAAs) as documented in our HIPAA Compliance Statement.
Who should enterprise procurement and legal teams contact for vendor evaluations?
Enterprise procurement officers, IT security evaluators, and legal counsel can direct compliance inquiries, vendor questionnaires, and custom contract requests to [email protected].
Enterprise Procurement & Legal Notice Actions
Questions Regarding COMEXCEL Policies or Compliance?
Our legal, compliance, and enterprise procurement specialists are available to assist with vendor due diligence, custom master service agreements (MSAs), BAA execution, and regulatory inquiries.